Security risk assessments are an important tool in your organization’s arsenal against cyber threats. They shine a spotlight on areas of risk in your digital ecosystem, inform and prioritize cyber risk mitigation strategies, and ensure hard-earned resources are allocated where they’re needed most. Assessments can also help you evaluate your third parties to mitigate the very real possibility that they’ll introduce unwanted risk into your organization.
As valuable as they are, security risk assessments are fraught with challenges. To complete them successfully, security teams must gather huge amounts of data from disparate tools – a highly manual process. That data must then be interpreted for actionable insights. This all takes time and can distract everyone from high-value tasks. If third parties are involved, risk assessment questionnaires must be collected and reviewed and may not even reveal the true extent of a vendor’s cybersecurity posture. Traditional assessments also only reflect a point-in-time and don’t account for evolving cyber security threats, vulnerabilities, and risk.
To properly conduct an internal or vendor security risk assessment, you need to combine automation with data-driven tools that provide a continuous, accurate picture of cybersecurity risk both internally and across your third-party ecosystem. It’s not as hard as it sounds. Let’s take a look at three ways to achieve this.
1. See your attack surface the way others do
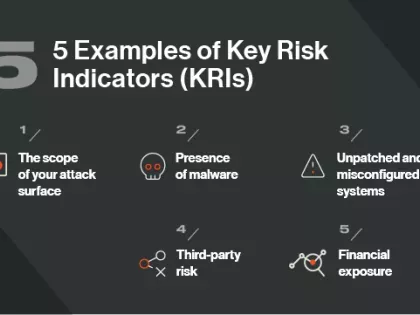
One of the biggest challenges to completing any security risk assessment is that digital ecosystems are expanding. The cloud, IoT, remote offices, and far-flung home-based employees have extended the attack surface beyond the network perimeter making it hard to pinpoint where cyber risk exists.
One way to close these visibility gaps is to continuously scan your attack surface so that you can see it the way the bad guys do. Use an attack surface scan to quickly validate your digital footprint, assess high areas of cyber risk exposure, and make informed, comparative decisions about where to focus your cybersecurity efforts.
For example, if your business has 100,000 records stored in an AWS cloud environment and the scan identifies 120 severe material findings, such as vulnerabilities or infections, then this environment should be prioritized for mitigation. However, a scenario where only three material findings are identified among a million stored records can be reprioritized if other more material findings are found.