CVE-2026-85385 Details
Concrete CMS below 9.5.4 did not validate the user timezone value (uTimezone) on write and rendered it without output encoding on the Dashboard user management page, where Date::getTimezoneDisplayName() returns any non-IANA value unchanged. A stored cross-site scripting payload saved in this field executed in an administrator's browser when they viewed the affected user in the Dashboard, running script in the admin session (for example to read CSRF tokens, create administrator accounts, or change site settings). In Concrete CMS 9.5.3 the field became reachable by unauthenticated visitors through public registration; in Concrete CMS below 9.5.3, the same field was reachable by any authenticated user through the account profile editor. Exploitation required concrete.misc.user_timezones to be enabled (off by default), and the unauthenticated path additionally required public registration to be enabled. The Concrete CMS security team gave this vulnerability a CVSS v4.0 score of 7.7 with vector CVSS:4.0/AV:N/AC:L/AT:P/PR:N/UI:P/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N. Thanks Suraj Bhosale for reporting.
View at NVD
Exploit prediction scoring system (EPSS) score for CVE-2026-85385
EPSS (Exploit Prediction Scoring System): EPSS predicts the likelihood that a vulnerability will be exploited in the wild. A higher percentage means a greater chance of an exploit occurring. The EPSS model produces a probability score between 0 and 1 (0 and 100%).
0.5 Probability of exploitation activity being observed over the next 30 days (43nd percentile)
CVSS score for CVE-2026-85385
CVSS (Common Vulnerability Scoring System): An open framework owned and managed by FIRST.Org, Inc. that assigns a numerical score from 0 to 10 to software vulnerabilities to indicate their severity.
9.6 Critical

CVE-2026-85385 Global Footprint

Top 10 Identified Countries

Country Observations Percentage
US 4,427 35.37%
DE 1,629 13.01%
JP 1,623 12.97%
GB 1,173 9.37%
NL 559 4.47%
CA 485 3.87%
FR 297 2.37%
CH 294 2.35%
AU 263 2.10%
PL 239 1.91%

Is CVE-2026-85385 part of your extended attack surface? Bitsight helps security leaders rapidly identify exposure and detect threats in order to prioritize, communicate, and mitigate risk.

View interactive product tours

CVE-2026-85385 Industry Footprint

Top 10 Identified Industries

*Service provider organizations (typically Technology and Telecommunications) are disproportionally represented in the results given their upstream ownership of end-user infrastructure. See our FAQs.

Industry* Observations Percentage
Technology 9,655 86.93%
Telecommunications 1,125 10.13%
Education 124 1.12%
Business Services 86 0.77%
Government/Politics 28 0.25%
Manufacturing 12 0.11%
Finance 12 0.11%
Transportation 12 0.11%
Media/Entertainment 11 0.10%
Energy/Resources 10 0.09%

Bitsight, the leading provider in Cyber Risk Management, introduced the next-generation internet scanner Bitsight Groma in May 2024. This technology continuously scans the entire internet to discover assets, collect asset attribution evidence, and identify an ever-growing set of security observations, such as vulnerabilities and misconfigurations. Groma’s scanning activities presently encompass:


  • 40 million-plus monitored organizations
  • 250 million-plus host names
  • 4 billion-plus routable IPv4 and IPv6 addresses

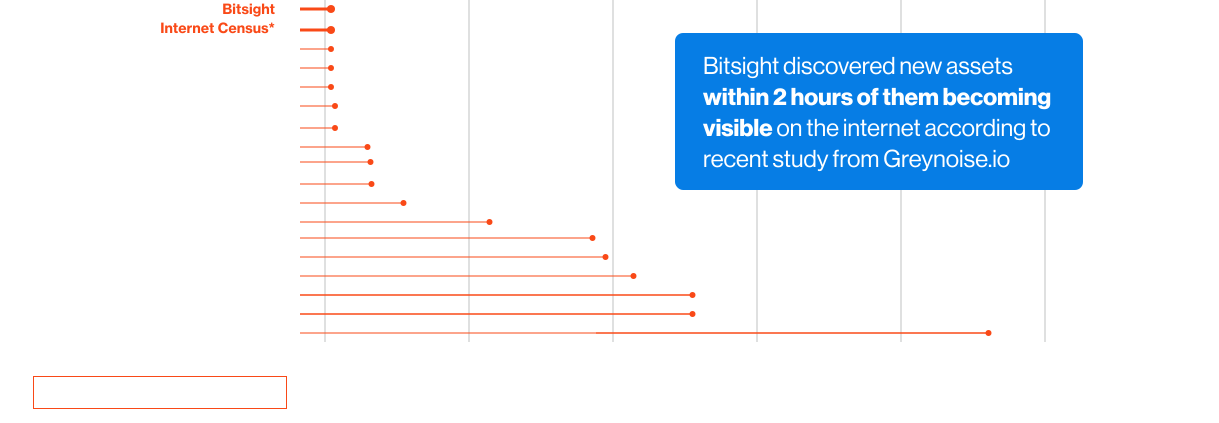
Greynoise’s recent study testifies the speed of Bitsight Groma.
Bitsight data discovery
Governance charcoal background

Bitsight TRACE team investigates security incidents and identifies vulnerabilities and threats.

View latest security research 

See what you’re up against across the expanding attack surface. Prioritize what matters most. And mitigate where you’re most vulnerable.

External Attack Surface Management