CVE-2026-75806 Details
Issue summary: An established DTLS 1.2 association using an AEAD cipher suite
can be terminated by a single unauthenticated datagram whose encrypted
fragment is shorter than the mandatory explicit IV and authentication tag
overhead.

Impact summary: An attacker who can send a datagram that is routed to an
existing DTLS 1.2 association can tear that association down without knowing
any key material. This is a Denial of Service limited to the targeted
association. There is no memory safety or confidentiality impact.

CWE: CWE-1284: Improper Validation of Specified Quantity in Input

Description: In TLS 1.2 and DTLS 1.2 every record protected by an AEAD cipher
suite carries an explicit IV followed by the ciphertext and an authentication
tag. When decrypting such a record the record layer passed the record length to
the cipher implementation before checking that the record was long enough to
contain the explicit IV and the tag. For a record shorter than that overhead the
cipher implementation rejected the impossible length, and the record layer
treated this as an internal failure and raised a fatal internal_error alert
instead of treating the record as one that failed authentication.

In TLS 1.2 the same record causes a fatal internal_error alert instead of the
expected bad_record_mac alert. Since any undecryptable record already
terminates a TLS connection, this is a protocol conformance issue rather than
a security issue in TLS.

The fix validates the record length against the explicit IV and tag length
before any AEAD processing, so that TLS reports bad_record_mac and DTLS
silently discards the record.

FIPS impact: no
The affected code is outside the FIPS module boundary.
View at NVD
Exploit prediction scoring system (EPSS) score for CVE-2026-75806
EPSS (Exploit Prediction Scoring System): EPSS predicts the likelihood that a vulnerability will be exploited in the wild. A higher percentage means a greater chance of an exploit occurring. The EPSS model produces a probability score between 0 and 1 (0 and 100%).
0.39 Probability of exploitation activity being observed over the next 30 days (32st percentile)
CVSS score for CVE-2026-75806
CVSS (Common Vulnerability Scoring System): An open framework owned and managed by FIRST.Org, Inc. that assigns a numerical score from 0 to 10 to software vulnerabilities to indicate their severity.
5.3 Medium
Products affected by CVE-2026-75806

CVE-2026-75806 Global Footprint

Top 10 Identified Countries

Country Observations Percentage
US 43,204 32.11%
JP 14,697 10.92%
DE 11,482 8.53%
NL 6,855 5.09%
CA 6,140 4.56%
FR 4,495 3.34%
GB 3,918 2.91%
CN 3,606 2.68%
KR 2,937 2.18%
IN 2,816 2.09%

Is CVE-2026-75806 part of your extended attack surface? Bitsight helps security leaders rapidly identify exposure and detect threats in order to prioritize, communicate, and mitigate risk.

View interactive product tours

CVE-2026-75806 Industry Footprint

Top 10 Identified Industries

*Service provider organizations (typically Technology and Telecommunications) are disproportionally represented in the results given their upstream ownership of end-user infrastructure. See our FAQs.

Industry* Observations Percentage
Technology 69,226 74.73%
Telecommunications 13,708 14.80%
Education 5,326 5.75%
Government/Politics 1,179 1.27%
Business Services 485 0.52%
Energy/Resources 393 0.42%
Media/Entertainment 298 0.32%
Manufacturing 253 0.27%
Utilities 244 0.26%
Finance 238 0.26%

Bitsight, the leading provider in Cyber Risk Management, introduced the next-generation internet scanner Bitsight Groma in May 2024. This technology continuously scans the entire internet to discover assets, collect asset attribution evidence, and identify an ever-growing set of security observations, such as vulnerabilities and misconfigurations. Groma’s scanning activities presently encompass:


  • 40 million-plus monitored organizations
  • 250 million-plus host names
  • 4 billion-plus routable IPv4 and IPv6 addresses

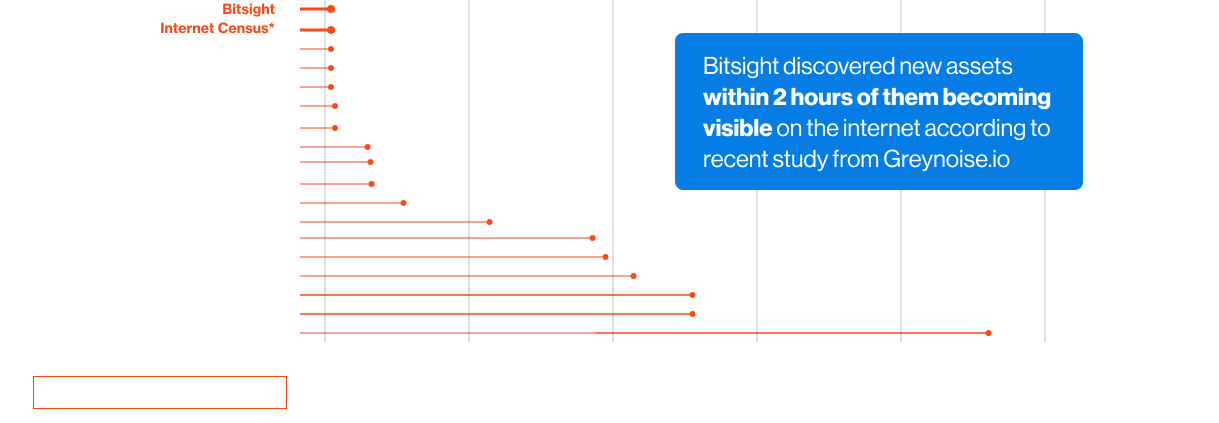
Greynoise’s recent study testifies the speed of Bitsight Groma.
Bitsight data discovery
Governance charcoal background

Bitsight TRACE team investigates security incidents and identifies vulnerabilities and threats.

View latest security research 

See what you’re up against across the expanding attack surface. Prioritize what matters most. And mitigate where you’re most vulnerable.

External Attack Surface Management