CVE-2026-73258 Details
Mongoose is an embedded web server and network library. Prior to 7.22, a remote attacker can place a lone carriage return or line feed in multipart input processed by mg_http_next_multipart() in src/http.c. The loops comparing s[b] and s[b + 1], and s[h2] and s[h2 + 1], use an incorrect AND condition and stop when either character resembles part of a CRLF terminator. This truncates headers, filenames, or boundaries and can cause an application to accept dangerous content after seeing a misleading Content-Type value. This issue is fixed in version 7.22.
View at NVD
Exploit prediction scoring system (EPSS) score for CVE-2026-73258
EPSS (Exploit Prediction Scoring System): EPSS predicts the likelihood that a vulnerability will be exploited in the wild. A higher percentage means a greater chance of an exploit occurring. The EPSS model produces a probability score between 0 and 1 (0 and 100%).
0.46 Probability of exploitation activity being observed over the next 30 days (38th percentile)
CVSS score for CVE-2026-73258
CVSS (Common Vulnerability Scoring System): An open framework owned and managed by FIRST.Org, Inc. that assigns a numerical score from 0 to 10 to software vulnerabilities to indicate their severity.
6.5 Medium
Products affected by CVE-2026-73258

CVE-2026-73258 Global Footprint

Top 10 Identified Countries

Country Observations Percentage
CN 99 21.62%
US 56 12.23%
BR 55 12.01%
DE 48 10.48%
KR 44 9.61%
VN 18 3.93%
TR 13 2.84%
MY 12 2.62%
PL 10 2.18%
IT 9 1.97%

Is CVE-2026-73258 part of your extended attack surface? Bitsight helps security leaders rapidly identify exposure and detect threats in order to prioritize, communicate, and mitigate risk.

View interactive product tours

CVE-2026-73258 Industry Footprint

Top 10 Identified Industries

*Service provider organizations (typically Technology and Telecommunications) are disproportionally represented in the results given their upstream ownership of end-user infrastructure. See our FAQs.

Industry* Observations Percentage
Telecommunications 219 66.97%
Technology 102 31.19%
Government/Politics 2 0.61%
Retail 1 0.31%
Utilities 1 0.31%
Energy/Resources 1 0.31%
Media/Entertainment 1 0.31%

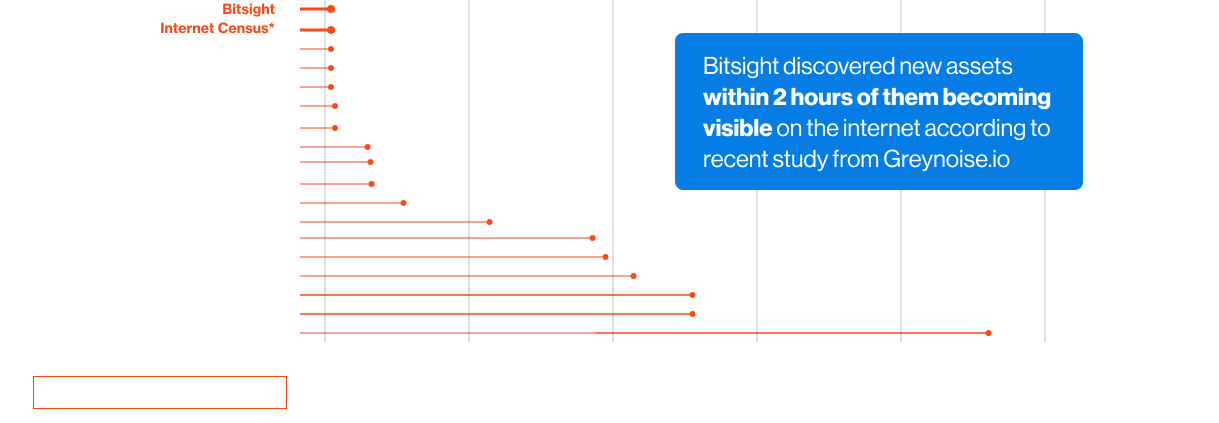
Bitsight, the leading provider in Cyber Risk Management, introduced the next-generation internet scanner Bitsight Groma in May 2024. This technology continuously scans the entire internet to discover assets, collect asset attribution evidence, and identify an ever-growing set of security observations, such as vulnerabilities and misconfigurations. Groma’s scanning activities presently encompass:


  • 40 million-plus monitored organizations
  • 250 million-plus host names
  • 4 billion-plus routable IPv4 and IPv6 addresses

Greynoise’s recent study testifies the speed of Bitsight Groma.
Bitsight data discovery
Governance charcoal background

Bitsight TRACE team investigates security incidents and identifies vulnerabilities and threats.

View latest security research 

See what you’re up against across the expanding attack surface. Prioritize what matters most. And mitigate where you’re most vulnerable.

External Attack Surface Management