CVE-2026-102411 Details
Allocation of Resources Without Limits or Throttling (CWE-770) in Elasticsearch can lead to Denial of Service via Excessive Allocation (CAPEC-130). Elasticsearch enforces a size limit on the user-supplied metadata field for each individual template resource, but does not limit the total memory used when multiple such resources are retrieved together. A user holding the *manage_index_templates* cluster privilege can register multiple resources each within the individual limit. Retrieving them together materializes all of their metadata values in memory at once, exhausting available heap and causing the affected node to fail with an out-of-memory error, resulting in a denial of service.
View at NVD
Exploit prediction scoring system (EPSS) score for CVE-2026-102411
EPSS (Exploit Prediction Scoring System): EPSS predicts the likelihood that a vulnerability will be exploited in the wild. A higher percentage means a greater chance of an exploit occurring. The EPSS model produces a probability score between 0 and 1 (0 and 100%).
0.31 Probability of exploitation activity being observed over the next 30 days (22nd percentile)
CVSS score for CVE-2026-102411
CVSS (Common Vulnerability Scoring System): An open framework owned and managed by FIRST.Org, Inc. that assigns a numerical score from 0 to 10 to software vulnerabilities to indicate their severity.
6.5 Medium

CVE-2026-102411 Global Footprint

Top 10 Identified Countries

Country Observations Percentage
CN 68 34.87%
US 26 13.33%
MX 16 8.21%
DE 12 6.15%
SG 10 5.13%
GB 8 4.10%
FR 7 3.59%
RU 6 3.08%
BR 5 2.56%
CA 5 2.56%

Is CVE-2026-102411 part of your extended attack surface? Bitsight helps security leaders rapidly identify exposure and detect threats in order to prioritize, communicate, and mitigate risk.

View interactive product tours

CVE-2026-102411 Industry Footprint

Top 10 Identified Industries

*Service provider organizations (typically Technology and Telecommunications) are disproportionally represented in the results given their upstream ownership of end-user infrastructure. See our FAQs.

Industry* Observations Percentage
Technology 129 92.14%
Telecommunications 8 5.71%
Retail 2 1.43%
Media/Entertainment 1 0.71%

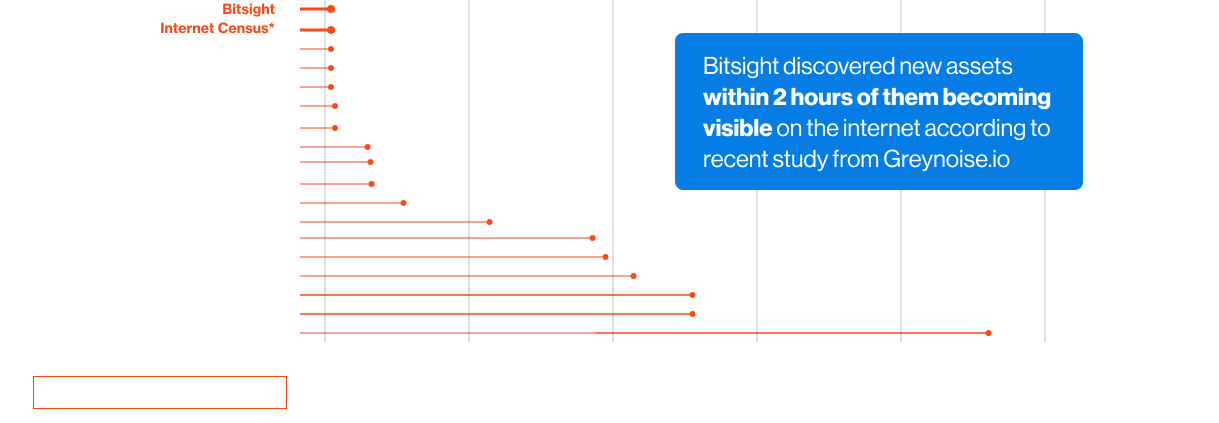
Bitsight, the leading provider in Cyber Risk Management, introduced the next-generation internet scanner Bitsight Groma in May 2024. This technology continuously scans the entire internet to discover assets, collect asset attribution evidence, and identify an ever-growing set of security observations, such as vulnerabilities and misconfigurations. Groma’s scanning activities presently encompass:


  • 40 million-plus monitored organizations
  • 250 million-plus host names
  • 4 billion-plus routable IPv4 and IPv6 addresses

Greynoise’s recent study testifies the speed of Bitsight Groma.
Bitsight data discovery
Governance charcoal background

Bitsight TRACE team investigates security incidents and identifies vulnerabilities and threats.

View latest security research 

See what you’re up against across the expanding attack surface. Prioritize what matters most. And mitigate where you’re most vulnerable.

External Attack Surface Management